Gnosis Pay Discloses Customer Data Breach Ahead of December 20 Closure
Card numbers, home addresses and linked crypto wallet details were exposed, while customer funds were unaffected.


Key Takeaways
- Gnosis Pay disclosed a data breach on November 6, 2026 affecting the legacy system behind its branded payment cards.
- Unauthorized access was detected on November 3, 2026, and containment began within two hours.
- Customer funds were unaffected, while card numbers, home addresses and linked wallet details were exposed.
- Mandatory 3D Secure checks stay in place until the consumer card system is retired on December 20, 2026.
Gnosis Pay disclosed a customer data breach on November 6, 2026, after hackers reached the legacy system behind its branded payment cards three days earlier. The intrusion exposed customer information, and Gnosis Pay said funds were unaffected.
What Data Was Exposed in the Gnosis Pay Data Breach
Card numbers, home addresses and the crypto wallets linked to customer accounts were among the exposed data, according to CoinDesk. One user said the leaked records tied a home address and card number to every wallet connected to the account. Gnosis Pay did not publish a customer count. Every affected customer received an email on November 6 with details of the information taken from their account. The intruders hit the consumer business that runs Gnosis Pay-branded cards. The enterprise platform that powers white-label card programs for other businesses was not affected.
How Gnosis Pay Responded
Monitoring systems detected the unauthorized access on November 3, 2026. Gnosis Pay said containment began within two hours, followed by the replacement of affected security credentials and a fix for the vulnerability. The company reported the breach to its partners and said it is communicating with the applicable data protection authorities and its card issuer. Card activity and wallets are under closer monitoring, and 3D Secure verification is now mandatory for all online card payments. The company said it is carrying out a full review and arranging specialist monitoring for signs that the exposed information is being misused. The Gnosis (GNO) project behind the payment platform published the disclosure on its own blog and on X.
The Consumer System Closes on December 20
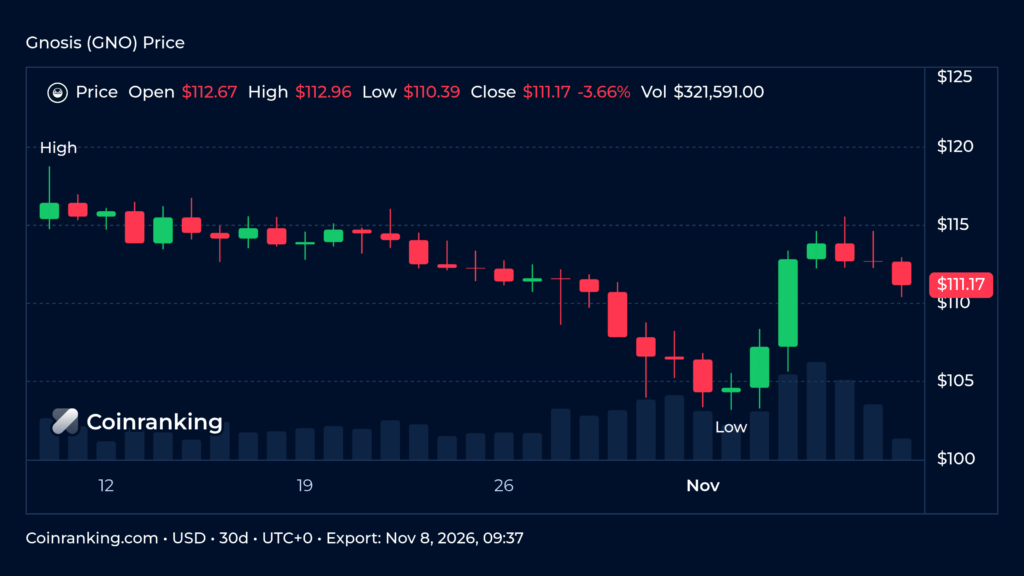
Gnosis Pay said the extra safeguards will remain until the consumer card system is retired on December 20, 2026. The closure was planned before the breach. The platform is one of the longest-running crypto payment card projects in the Ethereum ecosystem. Traders can watch the token through the period on the Gnosis price chart.
Frequently Asked Questions
What Happened in the Gnosis Pay Data Breach?
Hackers reached the legacy system behind Gnosis Pay-branded cards and exposed customer information including card numbers, home addresses and linked crypto wallets. Gnosis Pay disclosed the breach on November 6, 2026.
When Did the Gnosis Pay Breach Happen?
Gnosis Pay detected unauthorized access on November 3, 2026 and began containment within two hours. The public disclosure followed on November 6, 2026.
Were Funds Stolen in the Gnosis Pay Breach?
No. Gnosis Pay said customer funds were unaffected. The exposed data was customer account information, not wallet keys.
What Is the December 20 Closure of Gnosis Pay?
Gnosis Pay is retiring its consumer card system on December 20, 2026. The closure was planned before the breach, and extra payment checks stay in place until that date.
Is Gnosis Pay's Enterprise Platform Affected?
No. The intrusion hit the consumer business that runs Gnosis Pay-branded cards. The enterprise platform behind white-label card programs was not affected.
Sources
- Data breach in the legacy system behind Gnosis Pay-branded cards · Gnosis Pay
- Gnosis Pay breach exposes card numbers, home addresses and linked crypto wallets · CoinDesk
- Gnosis Pay discloses customer data breach ahead of Dec. 20 closure · crypto.news
Prices and market data: Coinranking.