Curve Finance CowSwapBurner Exploit Steals $38,206 in DAO Fee Revenue
The attacker forged 138 fee-sale orders by reusing one legitimate order signature, and the DAO vote to replace the vulnerable contract closes November 20.


Key Takeaways
- An attacker stole $38,205.76 in Curve DAO fee revenue on November 10, 2026 through 138 forged CoW Protocol orders.
- Curve published its security report on November 17, 2026 and said the stolen assets have not been recovered.
- The exploit reused one legitimate order signature because the CowSwapBurner contract did not compare it with the executed order.
- Curve DAO proposal 1524, which replaces the burner contract, is scheduled to close on November 20, 2026.
The Curve Finance CowSwapBurner exploit stole $38,205.76 in accumulated DAO fee revenue through 138 unauthorized transactions on November 10, 2026, according to the security report the protocol published on November 17. The stolen assets have not been recovered. User deposits in the protocol's liquidity pools, lending markets and crvUSD stablecoin were not affected, and Curve DAO Token (CRV) holders' funds were not targeted.
The CowSwapBurner is the contract that converts fees collected by Curve's pools and markets into crvUSD for the DAO, selling them through CoW Protocol every week. The attack hit collected protocol fees only. Curve's regular weekly conversion that week completed normally, delivering 97,317.74 crvUSD to the DAO.
How the Curve Finance CowSwapBurner Exploit Worked
The burner validates sale orders with the ERC-1271 signature standard. Curve's implementation checked the order described inside the submitted signature data, but it did not compare that description with the order actually executed, according to the detailed account of Curve's November 17 disclosure. The contract ignored the order hash parameter entirely.
At 00:07 UTC on November 10, seven minutes after the weekly exchange window opened, the attacker attached the signature data of one legitimate burner order to a different trade that sent the proceeds to an outside wallet. The same signature was then reused for 137 more trades covering 135 tokens. 133 of the forged orders had settled by 00:24 UTC, and the last unauthorized trade ran at 11:10 UTC. The median forged trade was worth about $254.
Where the Stolen Fees Went
Curve traced 37,611.76 USDC swapped for ETH within four hours of the first trade, split across four addresses and bridged to Arbitrum. About 37,229.89 USDC then reached Hyperliquid, where the funds were exchanged for 65.41 XMR and had not moved as of November 16. On November 15, the remaining 594 USDC moved through ETH into a 0.3 ETH deposit to Tornado Cash.
Blockchain analytics firm Bitquery reported separately that the same vulnerability was used against Balancer's fee burner on October 24, 2026, in 26 unauthorized trades worth about $1,512. Bitquery said it found no public Balancer disclosure of that incident and no on-chain transfers connecting the two attackers. Curve said the CowSwapBurner code had been reused by outside projects and that it notified operators of known derived deployments before publishing the vulnerability.
What Happens Next in the Curve DAO
Curve's Emergency DAO disabled fee collection and exchange operations on Ethereum on November 10 at 13:59 UTC after receiving an external vulnerability report, and took the same precautionary steps on Arbitrum and Base later that day. No fraudulent orders were found on Arbitrum or Gnosis. On November 17, residual balances from the old burner contracts were returned to the FeeCollector contracts.
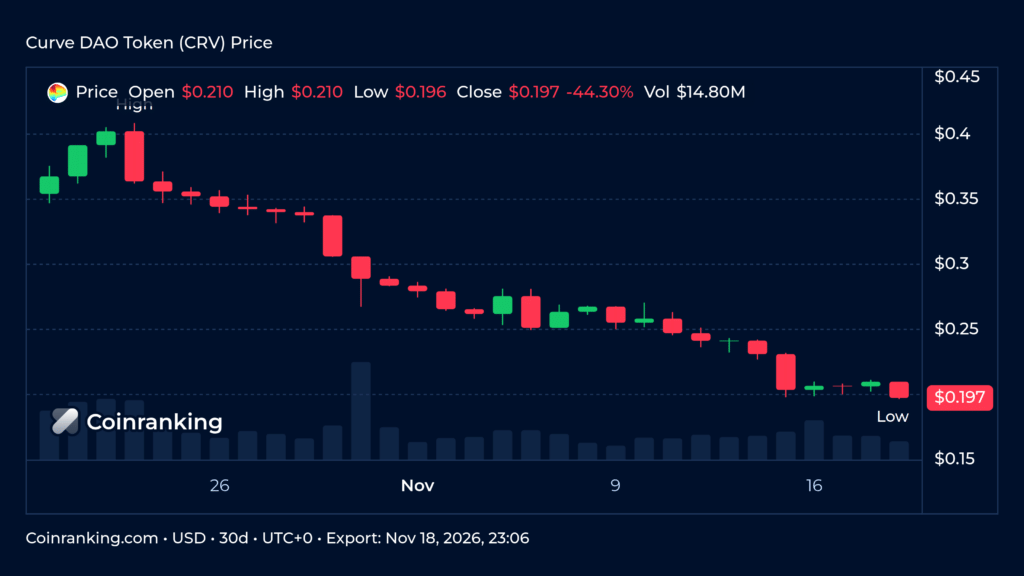
Ethereum fee conversions now sit paused while collected fees keep accruing, and Curve says those fees are not lost. Voting runs in Curve DAO proposal 1524, which opened November 13 and is scheduled to close November 20, 2026. The proposal asks holders of CRV, described in Coinranking's what Curve DAO Token is page, to replace the vulnerable CowSwapBurner with a contract that runs descending-price auctions and requires the validated hash to match the executed order. CRV traded around $0.197 on November 18, down about 44% over the past 30 days on the CRV 30-day chart.
Frequently Asked Questions
How Much Did the Curve Finance CowSwapBurner Exploit Steal?
$38,205.76 in accumulated DAO fee revenue, taken through 138 unauthorized transactions on November 10, 2026.
Were Curve User Funds Affected by the Exploit?
No. The attack targeted collected protocol fees. Curve said its liquidity pools, lending markets and crvUSD stablecoin were unaffected.
Has Curve Recovered the Stolen Funds?
No. Curve's security report published on November 17, 2026 said the stolen assets had not been recovered.
What Is Curve DAO Proposal 1524?
It is the vote that replaces the vulnerable CowSwapBurner contract with a descending-price auction version. It opened on November 13, 2026 and is scheduled to close on November 20, 2026.
Do CRV Holders Need to Do Anything after the Exploit?
No user action is required. Ethereum fee conversions are paused while the DAO votes on the replacement contract, and the fees collected meanwhile keep accruing.
Sources
- Curve DAO proposal 1524: replace CowSwapBurner · Curve DAO
- Curve Finance loses $38,206 in fee contract exploit · DaveFinances
- Prices and market data · Coinranking