Solana Warns Validators to Patch Critical Linux Kernel Bug Before Ubuntu Fix
The flaw is rated 9.8 out of 10 and every supported Ubuntu release is listed as vulnerable, with official fixes still in progress.

Key Takeaways
- Anza has warned Solana mainnet validators to urgently patch CVE-2026-98432.
- The Linux kernel flaw is rated 9.8 out of 10 and allows remote code execution through a multipath TCP listener.
- Ubuntu lists every supported release as vulnerable, with fixes marked as work in progress.
- Validators can disable multipath TCP as an interim mitigation until the official kernel update ships.
Anza, the infrastructure provider behind Solana, has warned mainnet validators to urgently patch CVE-2026-98432, a critical Linux kernel vulnerability rated 9.8 out of 10. The flaw allows remote, unauthenticated code execution on servers running a multipath TCP listener, and Ubuntu has not shipped an official fix.
What the Linux Kernel Flaw Does
The vulnerability sits in the Linux kernel's multipath TCP handling. According to the Ubuntu security tracker, every supported Ubuntu release from 16.04 through 26.10 is listed as vulnerable, with fixes marked as work in progress. Most Solana validators run Ubuntu, which is why Anza issued the warning to mainnet operators this week.
An attacker who can reach a validator server with a multipath TCP listener active could execute code without authentication, according to the report on Anza's warning. On Ubuntu 24.04 LTS the fix is in progress in kernel 6.8.0-149, and on 22.04 LTS in kernel 5.15.0-203, according to the tracker. No exploitation of Solana validators has been reported.
How Solana Validators Can Respond
Anza asked validators to apply interim mitigations while the kernel patch is in development. Disabling multipath TCP removes the interface the flaw targets. The measure is a workaround rather than a full fix, and operators are watching for the official Ubuntu kernel release.
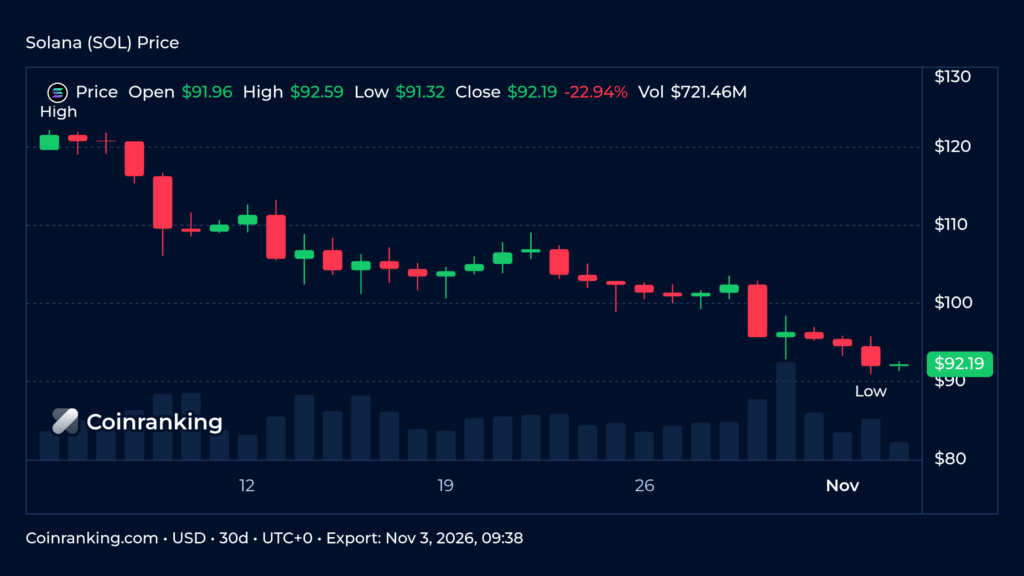
Solana is one of the largest layer 1 blockchains, and validators produce and validate blocks on the network, so server hardening is part of routine operations. Traders can follow the market response on the Solana price chart.
What Happens Next
The next milestone is the official Ubuntu kernel update. Once it ships, validators running standard Ubuntu packages can install it and remove the workaround. Until then, the interim mitigation is the available response, and Anza has asked operators to move quickly.
Solana (SOL) remains the native asset of the Solana ecosystem. No change to the protocol itself was announced alongside the warning.
Frequently Asked Questions
What Is CVE-2026-98432?
CVE-2026-98432 is a Linux kernel vulnerability rated 9.8 out of 10 that allows remote, unauthenticated code execution on servers with a multipath TCP listener. Anza warned Solana mainnet validators about it in November 2026.
When Will Ubuntu Fix the Linux Kernel Flaw?
Ubuntu's security tracker listed fixes as work in progress for every supported release as of November 2, 2026. No official release date for the patched kernel has been announced.
How Does the Linux Kernel Bug Affect Solana Holders?
The flaw targets the servers that run Solana validators, not wallets or tokens directly. Anza's warning covers mainnet validators running affected Linux kernels.
What Should Solana Validators Do about CVE-2026-98432?
Anza recommends disabling multipath TCP as an interim measure and installing the official Ubuntu kernel update as soon as it is released.
Does the Solana Network Need to Halt for the Kernel Fix?
No network halt has been announced. The warning covers server maintenance by individual validators, and the patch ships through normal Ubuntu kernel updates.
Sources
- Solana warns validators on Linux kernel bug, urges urgent action before Ubuntu fix · CoinMarketCap community (COINTURK News)
- CVE-2026-98432 | Ubuntu · Ubuntu security tracker
Prices and market data: Coinranking.