Ethereum Clients Teku and Besu Patch Flaw That Could Redirect Validator Rewards
Emergency releases drop certificates from a compromised authority after a forged certificate was shown to be able to send block rewards to an attacker.
Key Takeaways
- Teku 26.10.3 and Besu 26.10.2 remove certificates tied to a compromised certificate authority from their Docker images.
- A forged certificate could trick a validator into paying block rewards to an attacker's address.
- Default mainnet nodes are not affected and no exploitation has been reported.
- Operators running the clients outside Docker must also update their Java runtime and trusted certificates.
Ethereum (ETH) consensus client Teku and execution client Besu shipped emergency security updates on October 29, after a certificate authority compromise opened a path for attackers to redirect validator rewards.
What the Flaw Was
The updates, Teku 26.10.3 and Besu 26.10.2, remove trust in certificates linked to the compromised certificate authority eMudhra from the clients' Docker images. eMudhra is a certificate authority whose certificates sit inside the trust stores shipped with those images. The risk surface is any setup where a validator or a connected service communicates over HTTPS with a remote signer, a beacon node, an execution client, a builder or a relay. In those setups a man-in-the-middle could present a forged certificate and impersonate the service.
Teku said a deceived validator could end up proposing blocks that pay fees to the attacker's address, and that external signers face the highest forgery risk. Besu published the matching release notes on GitHub.
Who Is Affected
Default mainnet nodes are not affected, and the advisories and press coverage report no exploitation. The sharpest exposure is for operators running external signers or remote infrastructure over HTTPS. Those running Teku or Besu outside Docker must also update their Java runtime and trusted certificate stores, because the client update alone is not enough. The fix is mostly a trust store change, not a change to the protocol. Multiple reports note that Java 26 is no longer supported and should be replaced with Java 25.
Where This Leaves Validators
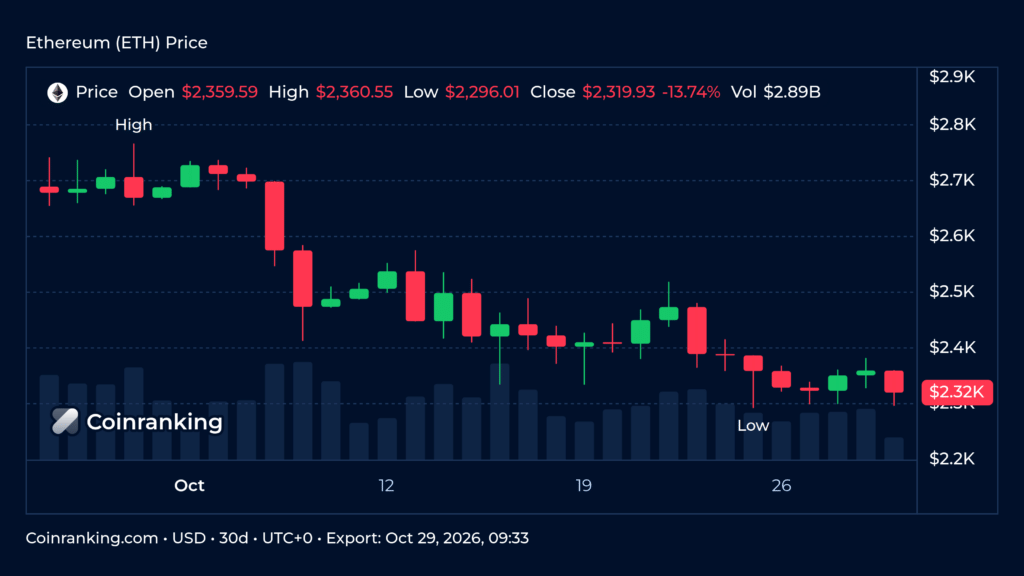
The episode shows how much of the validator stack now depends on ordinary web infrastructure. The staking coins market rests on validator setups that mix remote signers, relays and builders, and each HTTPS hop is a place where certificate checks matter. The Ethereum price chart on Coinranking tracked the market through the disclosure. CoinDesk first reported the patches in its coverage of the client fixes.
Frequently Asked Questions
Which Ethereum Clients Released Emergency Updates?
Consensus client Teku and execution client Besu, with releases 26.10.3 and 26.10.2 on October 29.
What Could an Attacker Do with the Forged Certificate?
Impersonate a connected service over HTTPS and trick a validator into proposing blocks that pay fees to the attacker's address.
Are Default Ethereum Mainnet Nodes Affected?
No. Default mainnet nodes are not affected, and no exploitation has been reported.
Sources
- Ethereum clients patch flaw that could let attackers redirect ETH rewards · CoinDesk
- Besu 26.10.2 release notes · Besu
- Ethereum Security Flaw Exposes Validator Reward Theft Risk; Teku, Besu Issue Emergency Updates · bloomingbit
Prices and market data: Coinranking.